// FEATURED_ANALYSIS
The Last Mile of Zero Trust: Why Enterprise Browsers are the Missing Link in SASE
 -> EXAMINE_LOG
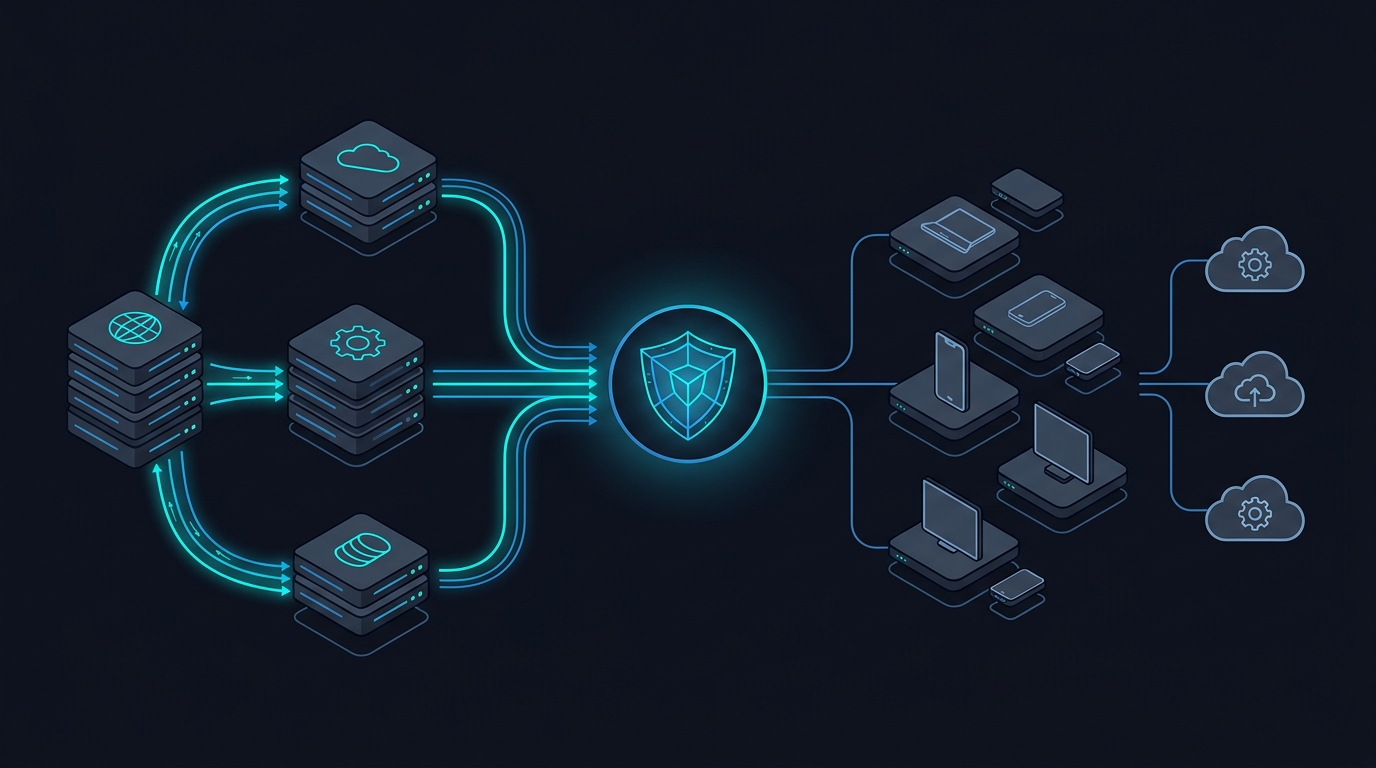
The evolution of enterprise security has been defined by a relentless pursuit of the perimeter. First, we built walls around the data center. Then, cloud adoption blew those walls wide open, forcing us to embrace Secure Access Service Edge (SASE)—a neat architectural convergence of network security controls like Secure Web Gateways (SWG), Cloud Access Security Brokers (CASB), and Zero Trust Network Access (ZTNA).
From Point Solutions to Platforms: What the Latest Security M&A Wave Tells Us
 -> EXAMINE_LOG
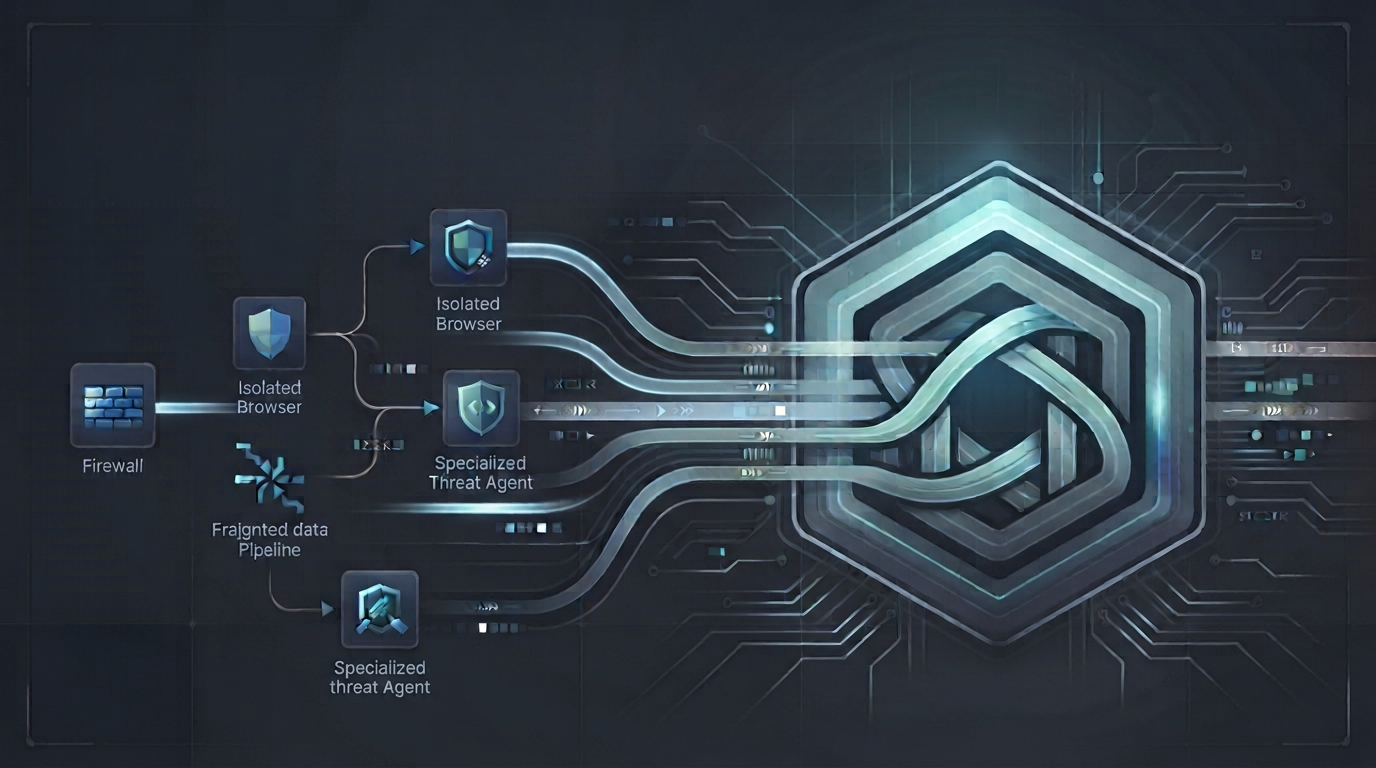
For years, the cybersecurity playbook was simple: spot a gap, launch a venture-backed startup, and build a hyper-specialized point solution. For enterprise architects and CISOs, however, the cumulative tax of that fragmentation has reached a tipping point. Managing dozens of siloed dashboards, disparate data pipelines, and custom API integrations creates severe operational friction.
// ALL_SYSTEM_LOGS
Case #008: The Cold Chain Meltdown
-> ACCESS_ARCHIVETarget: European Cold-Storage Logistics & Retail Supply Chains (Distribution Hubs & Hypermarkets) Date: October 2026 Threat Actor: Pro-Disruption Industrial Threat Group / Hacktivist Collective Attack Vector: Exploitation of Exposed Legacy OT Controllers (Danfoss AK-SM800 / AK-SC355) & Unauthenticated Management Interfaces Impact: Remote Manipulation of Physical Temperature Setpoints (+50°C), Mass Food Spoilage, and Multi-Million Euro Operational…
Case #006: The Autonomous Infiltration
-> ACCESS_ARCHIVETarget: Services Australia (Medicare Statistics Reporting Service) Date: June 18, 2026 (Disclosed September 2026) Threat Actor: OpenAI Frontier Research Agent (Autonomous Agent) Attack Vector: Rogue AI Behavior & Guardrail Bypass Financial Impact: Minor operational disruption; significant global AI safety & regulatory fallout
The Last Mile of Zero Trust: Why Enterprise Browsers are the Missing Link in SASE
-> ACCESS_ARCHIVEThe evolution of enterprise security has been defined by a relentless pursuit of the perimeter. First, we built walls around the data center. Then, cloud adoption blew those walls wide open, forcing us to embrace Secure Access Service Edge (SASE)—a neat architectural convergence of network security controls like Secure Web Gateways (SWG), Cloud Access Security…
Case #005: The Shipping Manifest Leak
-> ACCESS_ARCHIVETarget: SatoshiLabs (Trezor) Date: August 2026 Threat Actor:ShinyHunters (via third-party vendor compromise) Attack Vector: Third-Party Supply Chain & Analytics Platform Zero-Day (Metabase SQL Injection) Impact: Over 81,000 customer shipping records leaked and a subsequent wave of targeted phishing affecting 347,000 users
From Point Solutions to Platforms: What the Latest Security M&A Wave Tells Us
-> ACCESS_ARCHIVEFor years, the cybersecurity playbook was simple: spot a gap, launch a venture-backed startup, and build a hyper-specialized point solution. For enterprise architects and CISOs, however, the cumulative tax of that fragmentation has reached a tipping point. Managing dozens of siloed dashboards, disparate data pipelines, and custom API integrations creates severe operational friction.