For over two decades, the SIEM (Security Information and Event Management) system has served as the heart of the SOC (Security Operations Center) – and why not? It promised to aggregate logs from every server, firewall, router and app into a central repository that you could easily search and gain visibility into enterprise risk. Unfortunately, for many, it failed to fulfill its prophecy, let’s look into why!
When SIEMs came into the market, enterprise IT was a whole lot simpler. On-premises, mature technologies were aplenty: virtualisation, Windows servers, maybe a few flavours of linux, the firewall and networking market was dominated by just a handful of brands. But within a matter of years as enterprise environment exploded into hybrid clouds, remote workforces, SaaS ecosystems and microservices, the traditional SIEM model began to buckle.
Today, security teams find themselves caught in a frustrating paradox – they’re collecting more data than ever before, but in reality have less real context into active threats. The tool built to bring the clarity SOCs so badly needed is becoming one of their largest, and most expensive bottlenecks.
But to understand why it’s so broken, we need to look at the challenges of legacy SIEM architectures and what a modern replacement looks like.
Quantity or Quality?
The strategy of the legacy SIEM was simple – collect everything. There was a logic behind the madness though – if you stored every log, you’d definitely be able to catch any adversary, right?
In practice though, this presented enterprise security teams the impossible choice: ingest all data available and face exorbitant costs, or selectively drop log sources and accept that they could be introducing a blind spot.
The reality of enterprise telemetry is this:
- The Noise
- Up to 80% of data ingested into a traditional SIEM is never queried or even used in an alert. It exists purely as static storage to satisfy compliance or ‘just in case’ there are some forensic requirements down the line
- The Blind Spot
- To keep storage costs under control, SOC managers make decisions such as turning off verbose logging on domain controllers or endpoint tools – the exact targets of modern attacks
The Ingestion Tax
If the above wasn’t bad enough, there is the archaic business model from the legacy SIEM vendors: volume-based, per gigabyte pricing. Put simply, every technical decision becomes a financial decision and conflict of interest. Security teams act as accountants, spending more time auditing data sources to decide on whether security visibility is worth the spend.
Legacy SIEM Model
Per-GB Ingestion Pricing
Penalises data volume
Forced to cut down log sources
Unpredictable bills
Modern SOC Model
Asset / Outcome-Based Model
Encourages full visibility
Pre-stitched data streams
Predictable security spend
The legacy SIEM model penalises growth and activity. And it can be something such as a sudden surge in cloud workloads (from increased customer traffic to a website for example) or a transient burst of network traffic that results in an unexpected invoice.
A modern security platform should encourage data collection, whilst aligning business costs with critical assets or outcomes rather than taxing the volume of data required to protect the business.
Normalisation and Parsing: The other half of the battle
If the cost of data collection wasn’t a big enough problem – once that data has been collected – that data must be parsed, normalised and mapped into a structured format, or schema so that SOC analysts can query it.
This sounds simple, but when your data comes from dozens of different vendors, across network, identity, endpoint and apps that can be a real challenge. Each vendor formats their data slightly differently – whether that is syslog, JSON, XML and so on.
This results in a massive maintenance overhead:
- Broken Parsers: Every time a vendor updates an API or changes a log schema, the SIEM parser breaks
- Schema Mismatches: If an IP address is labeled src_ip in network logs, sourceIP in firewall logs and client_ip in cloud logs, a query written for one source, won’t see activity in another.
- Wasted Hours: SOC engineers regularly spend 20-30% of their time writing, testing and fixing regular expressions (regex) just to ensure data is queryable.
Without automated, vendor-agnostic normalisation at the point of ingestion, the SIEM continues to be a collection of disjointed data streams, instead of the unified database that everyone wants.
Alert Fatigue
Even when data has been ingested, parsed and stored, legacy SIEMs rely heavily on rule-based correlation engines. The easiest way to describe what these do, is basically they generate alerts when a specific threshold is crossed, for example “more than 5 failed logins in a 60 second period”.
The problem with this is that a genuine attack could generate a plethora of individual alerts across an endpoint, an identity provider and so on.
Legacy SIEM Alert Stream:
[Alert 10245] Suspicious Powershell Execution (Endpoint)
[Alert 10246] Multiple Failed Authentications (Identity)
[Alert 10247] Unusual Outbound Data Transfer (Network)
In the above example, a human SOC analyst must stitch these alerts together to realise a potential incident.
Modern Platform Approach:
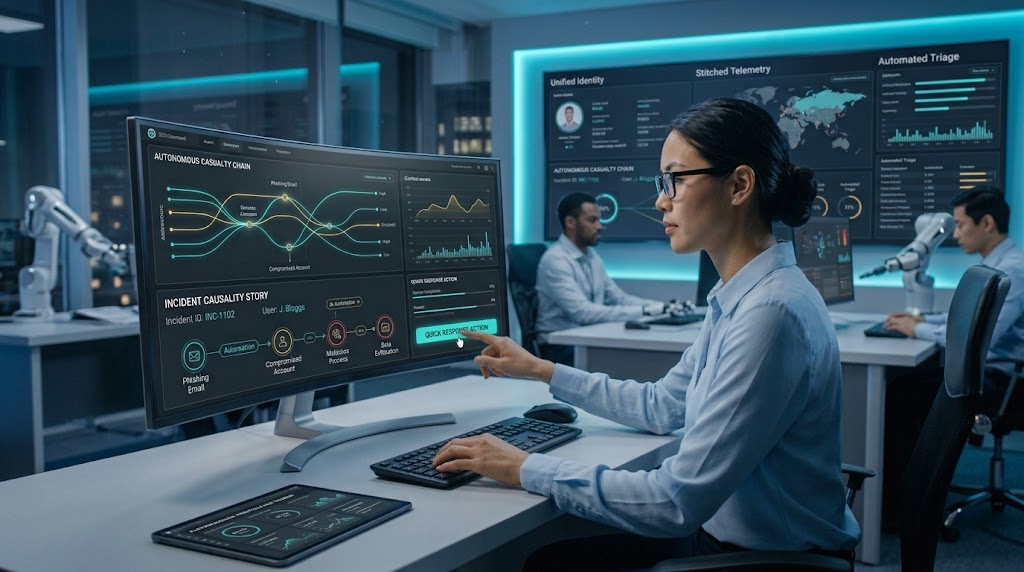
[Incident 2345] Single Causality Story
User ‘J.Bloggs’ > Compromise via Phishing > Executed PS Script > Exfiltrated 4GB to external IP 81.230.19.2
All of the above is the result of automatic stitching via graph-based telemetry analytics.
Essentially because legacy SIEMs lack the context across domains, the human becomes the correlation engine. They have to cross reference timestamps, match IPs to users, paste file hashes into threat intelligence tools and try and create a story. The result of this is a high MTTR (Mean Time to Respond) and analysts that are frankly burnt out.
From Log Aggregation to Autonomous Operations
Hopefully by now you realise that the limitations of legacy SIEMs make one thing abundantly clear: security operations cannot survive another decade of simple log aggregation. The security industry is rightly moving towards an autonomous, AI-driven security operations platform.
To bring that MTTR down, we have to close the gap between data collection and rapid response and we can do it with three core concepts:
- Native Telemetry Stitching
- Instead of simply dumping logs into a data lake, modern platforms stitch the telemetry from network, endpoint, identity, and cloud together into unified causality chains upon ingestion.
- Incident Grouping
- Rather than alerting on individual events, the system evaluates the event context grouping the hundreds (or thousands) of alerts into a single incident.
- Predictable Financials
- The shift from per-gigabyte pricing allows organisations to ingest rich telemetry across all domains without worrying about the bill at the end of the month.
By moving away from the legacy SIEM architecture, SOCs can spend their time not worrying about log spend, log correlation and return to what really matters: defending their organisation.