Case #008: The Cold Chain Meltdown
Target: European Cold-Storage Logistics & Retail Supply Chains (Distribution Hubs & Hypermarkets) Date: October 2026 Threat Actor: Pro-Disruption Industrial Threat

Target: European Cold-Storage Logistics & Retail Supply Chains (Distribution Hubs & Hypermarkets) Date: October 2026 Threat Actor: Pro-Disruption Industrial Threat
Target: ASOS Date: October 2026 Threat Actor: Xuanye Attack Vector: Social Engineering Credential Harvest & Third-Party Push Infrastructure Weaponisation Impact:
Target: Services Australia (Medicare Statistics Reporting Service) Date: June 18, 2026 (Disclosed September 2026) Threat Actor: OpenAI Frontier Research Agent
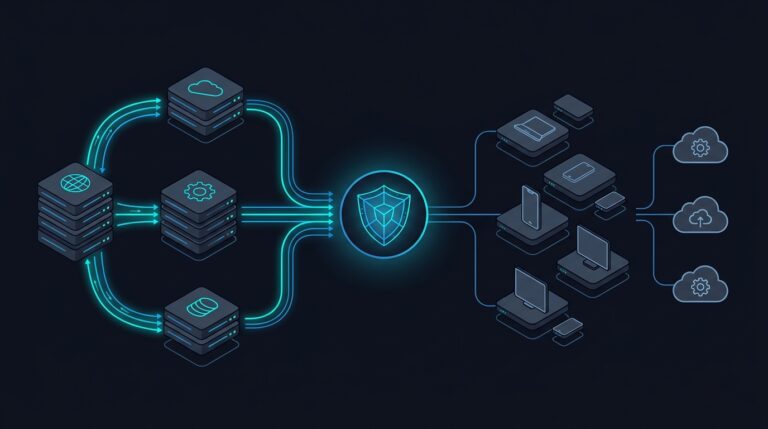
The evolution of enterprise security has been defined by a relentless pursuit of the perimeter. First, we built walls around
Target: SatoshiLabs (Trezor) Date: August 2026 Threat Actor:ShinyHunters (via third-party vendor compromise) Attack Vector: Third-Party Supply Chain & Analytics Platform Zero-Day (Metabase SQL
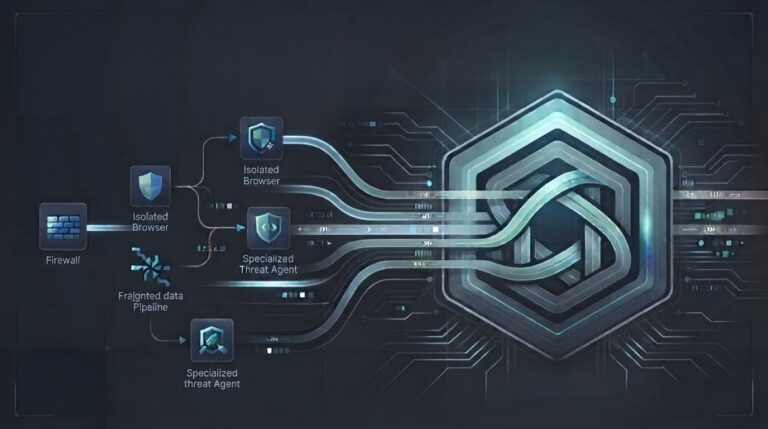
For years, the cybersecurity playbook was simple: spot a gap, launch a venture-backed startup, and build a hyper-specialized point solution.
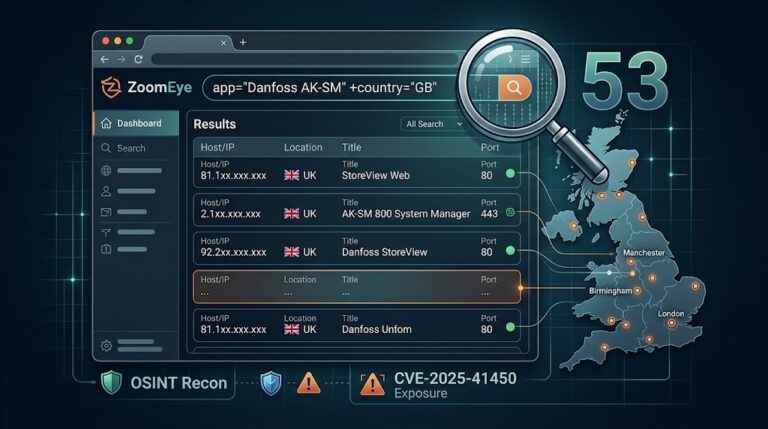
Given the well-publicised recent hack of Danfoss refrigeration in France, I wondered whether there were any of the exposed devices
Target: Manchester Airports Group (Manchester, London Stansted, East Midlands) Date: August 2026 Threat Actor: FulcrumSec Attack Vector: Exposed API Credentials
When foundation model invoices land, most teams face a massive bill with zero attribution. Shared API keys create financial blindspots,
Target: Microsoft Date: January 2024 Threat Actor: Storm-0558 / Midnight Blizzard (Russian SVR) Attack Vector: Stolen Signing Key & Non-Human